
Critical Orkes Conductor Vulnerability Exploited in Attacks
CVE-2026-58138 is an unauthenticated remote code execution vulnerability that attackers can exploit via inline workflow definitions. The post Critical Orkes Conductor Vulnerability Exploited in Attacks appeared first on SecurityWeek.
AI systems don’t have a drive to survive. Here’s why
In controlled safety tests described earlier this year, researchers asked AI models to solve a series of simple math problems. Partway through the exercise, the instructors warned the bots that if they tried to solve the next problem, the computer environment they...
Royal Society slams UK.gov science shake-up
The president of the Royal Society has slammed the government’s decision to move science policy from the department also covering technology to the business department. In changes announced after Andy Burnham became UK Prime Minister in July, the government abolished...
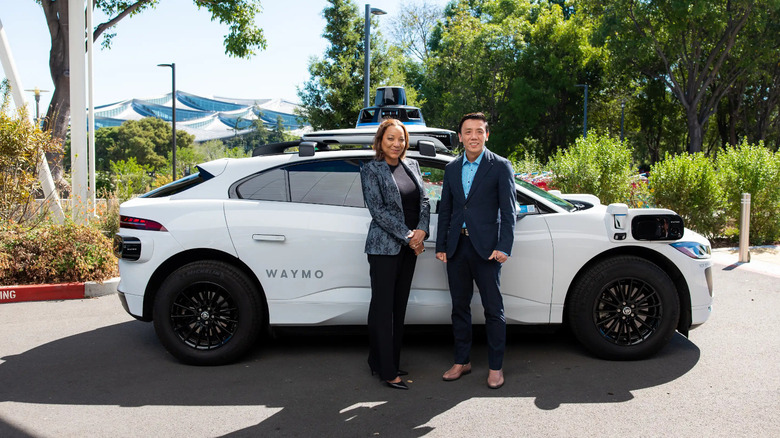
Waymo is expanding to Singapore
Waymo has announced its next international location: Singapore.
TV Audio Tube Makes a Transceiver
It’s not often we see a tube project here, so [Helge Fykse]’s PCL86 transceiver is a welcome find. If you know anything about the European Pro-Electron device naming system you’ll be familiar with it as it applies to tubes. The first letter denotes the heater...
MIND Secures $72 Million for AI-Powered DLP
The company will use the funding to accelerate platform development and expand its presence in key enterprise markets. The post MIND Secures $72 Million for AI-Powered DLP appeared first on SecurityWeek.
Check Point, Kaspersky, Tanium Patch Product Vulnerabilities
Check Point Security Management and Log Servers are affected by a critical vulnerability that can allow remote code execution with root privileges. The post Check Point, Kaspersky, Tanium Patch Product Vulnerabilities appeared first on SecurityWeek.
On Call: Techie fixed Wi-Fi dead zone with a drill
ON CALL Welcome to another edition of On Call, The Register's reader-contributed column that celebrates the fine art of tech support. This week, meet a reader we'll Regomize as "Eddy," the one-person IT department for an assisted living company. "I have had quite a...
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that's assessed to be operated by China-based threat actors and features an artificial intelligence (AI)-powered system to navigate and control compromised devices. "Distributed primarily via...
Jemalloc 5.4.0
Article URL: https://github.com/jemalloc/jemalloc/releases/tag/5.4.0 Comments URL: https://news.ycombinator.com/item?id=49750152 Points: 6 # Comments: 0
AWS confesses its console causes cloudy confusion for new users
Amazon Web Services does a lot of things right, but the cloud giant’s user console is arguably not one of them. Which may be why it’s just created an easier alternative for new users. In a Wednesday post, Senior Solutions Architect Micah Walter said that when AWS...
USA’s Venezuela takeover comes with bonus exposure to Chinese AI surveillance tech
Think tank the Australian Strategic Policy Institute (ASPI) has warned that Venezuela is poised to adopt Chinese AI systems to enhance surveillance systems that already rely on Middle Kingdom tech, and called for US Secretary of State Marco Rubio to do something about...
AI risks make some insurers wary of corporate liability
If AI does end up killing us all, or just compounds our daily havoc, the insurance industry would rather not pay the bill. "AI-related harms are already emerging, including incorrect or misleading outputs, deepfakes, privacy violations, intellectual property disputes,...
The Scourge of x86 Emulation
Article URL: https://fex-emu.com/Scourge-of-emulation/ Comments URL: https://news.ycombinator.com/item?id=49750094 Points: 6 # Comments: 0
Everyone thought AI would replace junior engineers. We’re hiring more of them
The biggest hiring myth in tech is that AI is making junior engineers obsolete. The logic seems sound: AI can write code, so why hire people to write more of it? Junior engineers have always learned on the job, fixing bugs and shipping small features until they build...
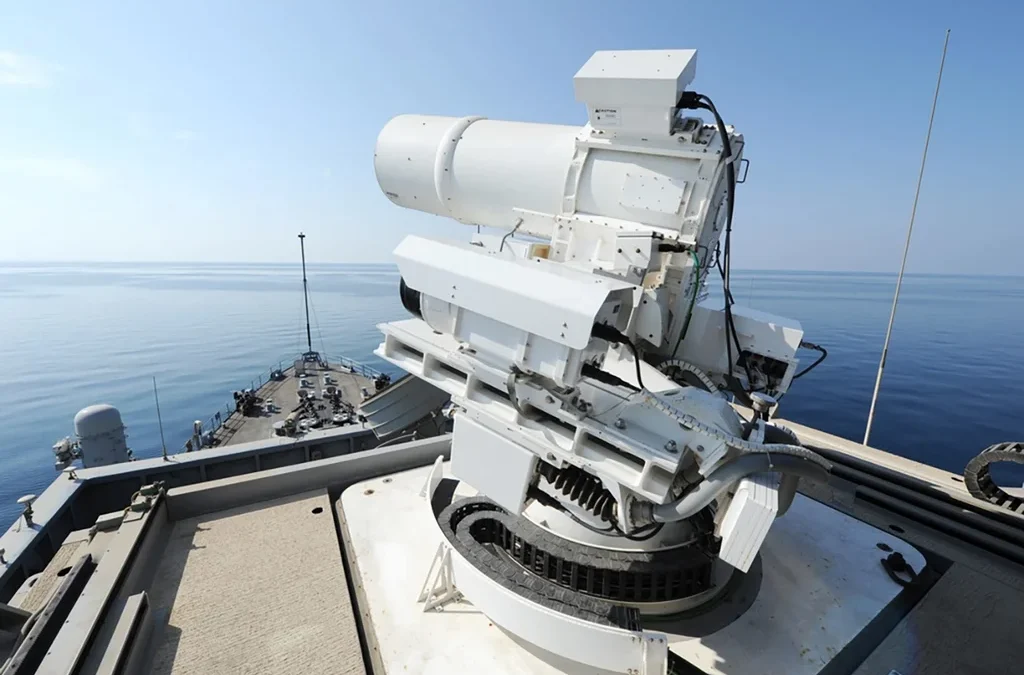
The Navy’s push for shipboard laser weapons just got a new entrant
This article is republished with permission from Laser Wars, a newsletter about military laser weapons and other futuristic defense technology. The U.S. Navy has awarded a modest contract to America’s largest shipbuilder for a new high-energy laser weapon for maritime...
Building a DIY Centrifuge For Blood Processing
If you want to do certain types of lab work with blood, you’ll need a centrifuge. It’s often possible to find serviceable units on the used market, but they may not meet your requirements if you’re doing something quite specific. For that reason, [Thomas Nguyen]...
Waymo in Singapore
Article URL: https://waymo.com/waymo-in-singapore/ Comments URL: https://news.ycombinator.com/item?id=49749981 Points: 5 # Comments: 1
Pre-Greek: The lost language hidden within Ancient Greek
Article URL: https://linguisticdiscovery.com/posts/pre-greek/ Comments URL: https://news.ycombinator.com/item?id=49749771 Points: 3 # Comments: 0
Code Scans
Article URL: https://devin.ai/blog/introducing-code-scans Comments URL: https://news.ycombinator.com/item?id=49749744 Points: 3 # Comments: 0
Hacking OpenAI
Article URL: https://www.hacktron.ai/blog/hacking-openai Comments URL: https://news.ycombinator.com/item?id=49749656 Points: 10 # Comments: 1
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point's Security Management and Log Servers could allow an attacker without login credentials to run code as root on those servers over the network. The Security Management Server is the system that controls firewall policy and...
ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Attackers keep finding new keys. The funny part is that defenders keep inventing where to store them. This week, those keys sit in AI tools, exposed services, old bugs, weak logins, and software sold like a monthly subscription. Some attacks use new tricks. Others...
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere else on the host, Docker warns in a security announcement on September 15. The escape runs with the rights of...
Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE. "HEAVYGRAM offers builtin commands supporting remote command execution, system,...
Ask A Monk – A digital wilderness for thoughts with no immediate answer
Article URL: https://askamonk.online Comments URL: https://news.ycombinator.com/item?id=49749171 Points: 3 # Comments: 0
Telstra outage: The night a network decided the year was 2006
Article URL: https://www.netnod.se/blog/telstra-outage-night-network-decided-year-was-2006 Comments URL: https://news.ycombinator.com/item?id=49748957 Points: 9 # Comments: 2
Claude Code from Source
Article URL: https://claude-code-from-source.com/ Comments URL: https://news.ycombinator.com/item?id=49749019 Points: 12 # Comments: 1
Surveillance Camera Security? It’s Completely Flocked!
Surveillance cameras from Flock Safety have become a controversial privacy battleground, as the communities in which they are installed wake up to their sinister potential, and stories roll in of law enforcement professionals abusing their access. One has had its disk...
Goose: 1.16x faster than C++ and 1.12x than safe Rust, while memory safe
Article URL: https://github.com/aardappel/goose/tree/master Comments URL: https://news.ycombinator.com/item?id=49748954 Points: 10 # Comments: 3