
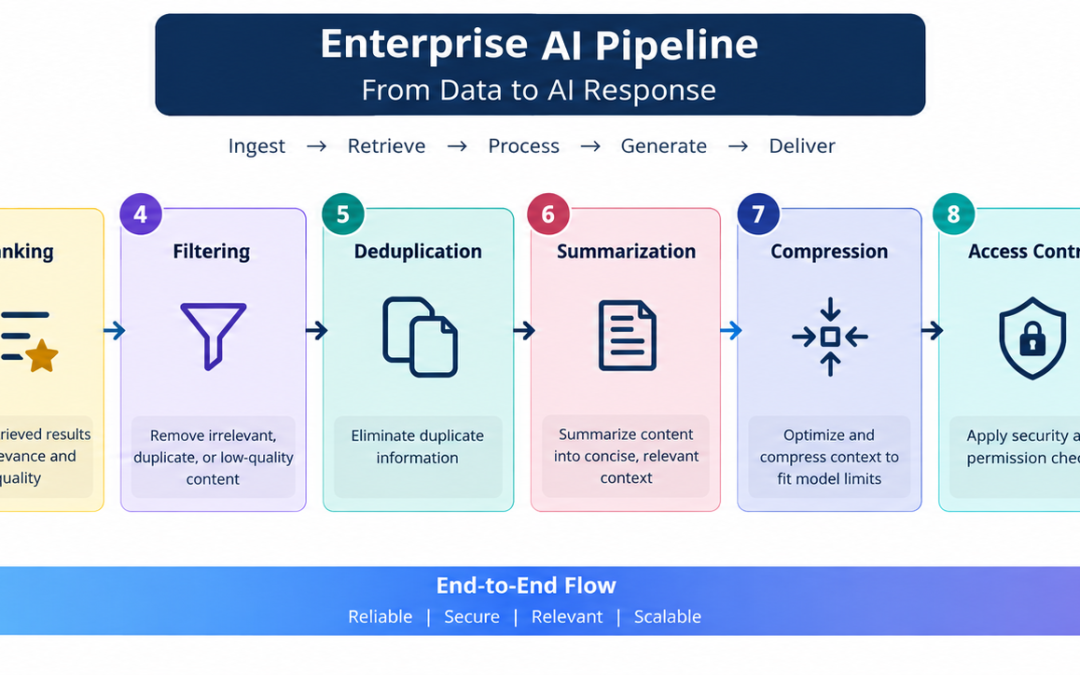
Building Enterprise Context Pipelines: Retrieval, Orchestration, and Cloud-Native Architecture
From Principles to PipelinesIn Part 1, we made the case that an AI system is only as effective as the information it receives, and we described what makes context reliable: relevance, freshness, completeness, trustworthiness, and authorization. Those five dimensions...
Teams Are Moving from Closed-Source APIs to Open-Source Models in 2026
By now, fellow agent builder, you’ve probably heard that open-source models have caught up to the proprietary ones from Google, Anthropic, OpenAI, and the like. But, here’s something you may have missed: teams are actually moving away from closed-source APIs to...
Why Browser Agent Handoffs Need More Than a Timeout
Designing a browser handoff means separating permission, local execution, and effects that a local scheduler cannot undo. Imagine a browser agent clicking Save in an administration interface. Before the confirmation arrives, its permission to control the browser...
AI Coding Agents Changed What I Review in ML Apps
For a while, my workflow for building ML applications with coding agents looked something like this: Write a prompt. Wait for the agent to make changes. Open the diff. Read the code. Try to understand what changed. Run it. Repeat. At the beginning, this worked...
How to Test Product Hypotheses When Your User Base is Tiny
Chances are you, as a product manager or a startup founder, took some time to learn about designing A/B tests to make informed decisions about which features land, and which need to be thrown in the bin. But there’s one thing you may have noticed doing a Coursera...
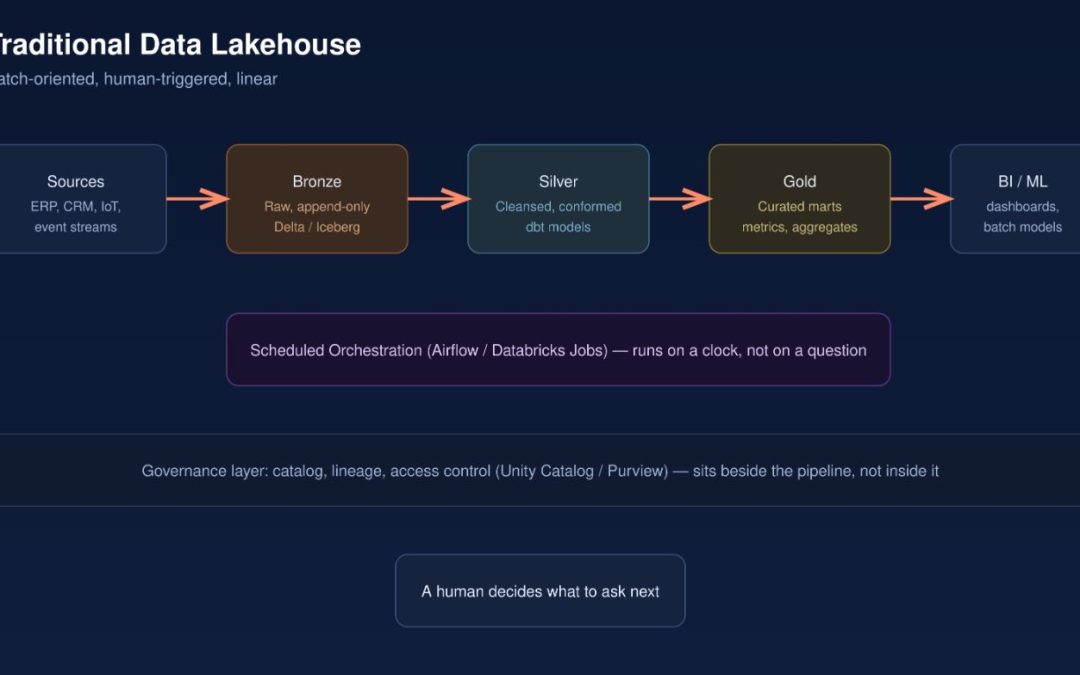
The Lakehouse Wasn’t Built for AI Agents
I have spent a good chunk of the last few years building and defending medallion lakehouses. Bronze, silver, gold, the whole ritual. And honestly, it works. It is a genuinely good pattern for turning messy operational exhaust into something a BI team can trust. But...
A Green API Is Not a Working Page
I spent a morning connecting a session-recording tool to a product search engine I run, expecting to learn something about user behaviour. Instead it handed me a list of JavaScript errors, and every single one turned out to be a bug that had been in production for...
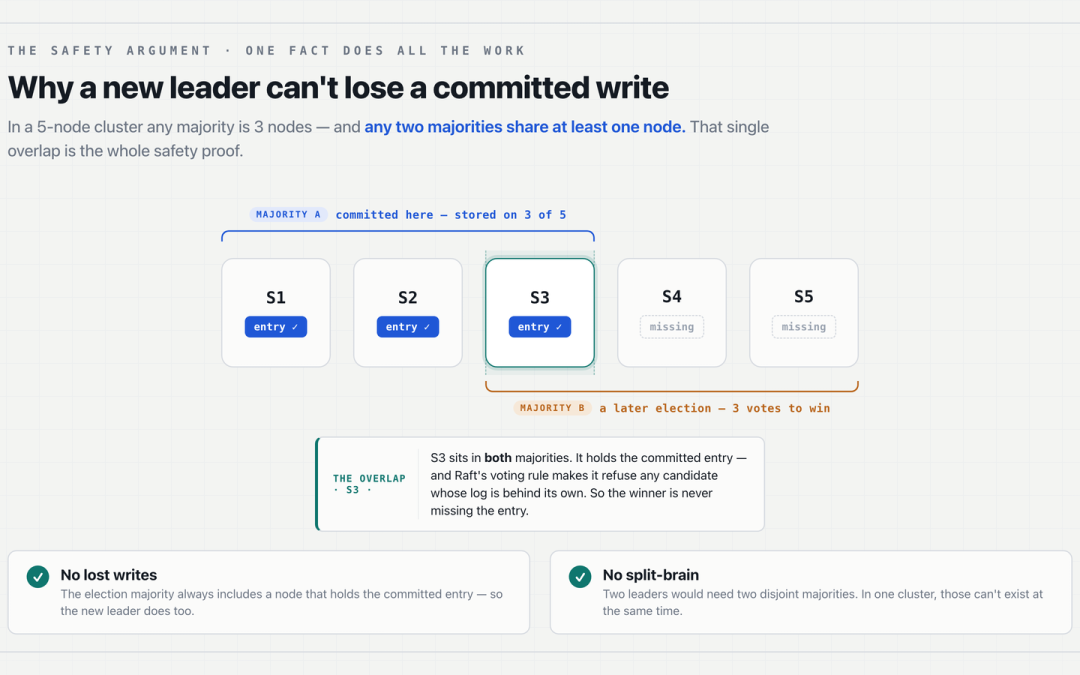
Why a Healthy Cluster Refuses Your Writes: A Working Model of Raft
You don't implement consensus, but you operate it every day — etcd, Consul, CockroachDB, Kafka's KRaft. This is the mechanism behind the elections, the read-only clusters, and the fsync obsession: enough Raft to turn its surprises into diagnoses.The cluster is up....
HTTPS for Music: Who Plays the Certificate Authority?
Twenty years ago, most of the web ran in the clear. Anyone on the path could read the page, and nobody could prove which server they were talking to. The fix was not a law and not a detector. It was a protocol with a trust layer around it, and today a padlock in the...
Engineering Debt at Scale: Three Structural Failures in Production AI Systems
Most of what breaks AI systems in production has nothing to do with the model.I spend a good chunk of my job reviewing code: production systems and open-source contributions as an engineer, plus the code behind systems and software papers as an academic peer reviewer....
CineGeist: A Movie Recommender for People Who Can’t Describe Their Taste
I built a movie recommender for people who can't describe their own taste, a dead feature taught me a lot about dense vector spaces. It is often difficult for people (me) to say what films they really like when asked. It's not a malicious lie, but something that is...
Maximize your Colosseum Build with SODAX as Your Cheat Code
You have a weekend, maybe two. You have an idea that works on Solana. And now Colosseum has told you that idea could also compete for prize money on Ethereum, Hyperliquid, Base, Arbitrum, Robinhood Chain and more, if you can get it there in time.That's the actual...
The Real AI Alignment Problem Is the Race Itself
AI researchers are quitting, labs are talking about slowing down, governments are worried about China, and everyone has an incentive to keep accelerating anyway. Maybe we have been looking at the AI alignment problem one layer too low. We keep asking whether we can...
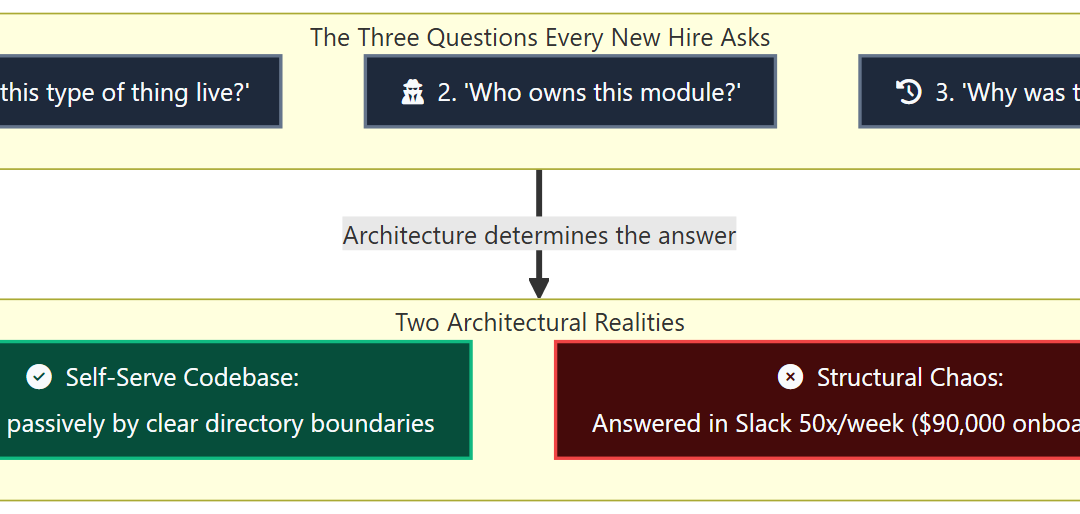
The $90,000 Onboarding Tax Hidden Inside Messy Codebases
The Question Nobody Asks Out LoudThere is a question that surfaces in every engineering team, in every company, in every codebase larger than a weekend project:“Where does this go?”Not where should it go in theory. Where does it actually belong right now, given the...
The Marketplace Betting AI Won’t Kill Human Advice
1. What is your company in 2–5 words? Human expertise, on demand. 2. Why is now the time for your company to exist? Trust is the scarce resource online right now. Anyone can claim expertise, and AI has made generic advice free. ExpertEase exists to make trusted human...
Cursor Can Write the Code, but You Still Need the Plan
Working with Cursor can feel a little like having a whole engineering team sitting next to you. You can ask it to explore a codebase, write a feature, create tests, fix bugs, and connect different parts of an application. It can even break larger tasks into agents,...
Grok Voice Realtime: xAI’s Audio-to-Audio Model Explained
Overviewgrok-voice/realtime is maintained by xai. grok-voice/realtime is an xAI Grok audio-to-audio model exposed through fal as fal-ai/grok-voice. It accepts a user speech recording, applies optional system instructions and tool configuration, and returns the agent’s...
The Ultimate Resource Guide for Awards, Recognition, and Industry Research
A collection of useful resources for researching, comparing, and navigating awards and recognition programs, including databases, guides, and other resources for creators, professionals, and organizations. Interviews & Conversations Interviews I’ve done about...
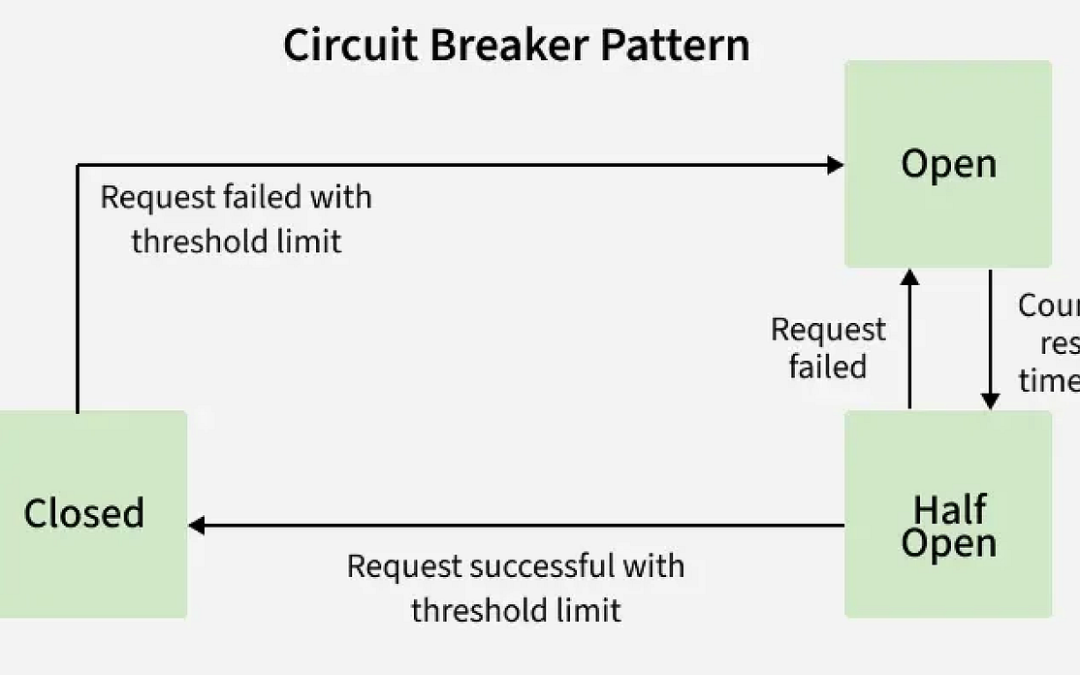
Circuit Breakers: How to Stop One Service Failure From Taking Down Your System
What happens when one service fails, but your entire system keeps calling it anyway ? Imagine your payment service is down. Normally, every purchase request follows a path like this: User ↓ Order Service ↓ Payment Service ↓ Bank Now the Payment Service is unavailable...
How to Cut Your AWS SQS Costs Without Redesigning Your Architecture
SQS is a very popular and cheap service from AWS which seems pretty inoffensive to your monthly bill. However, it charges per request, not per message, and that detail is where most of the waste hides. Things like racking up old and unused queues with live consumers,...
CISA Gives Agencies 3 Days to Patch Exploited Pixel Zero-Day
Google says a Pixel modem zero-day was under targeted exploitation. CISA has added CVE-2026-58704 to KEV as users are urged to patch. The post CISA Gives Agencies 3 Days to Patch Exploited Pixel Zero-Day appeared first on TechRepublic.
Brevo Supply Chain Attack Injects Malware Into 100,000 Websites
Hackers used a compromised API key to deploy a Cloudflare worker that injected malicious scripts. The post Brevo Supply Chain Attack Injects Malware Into 100,000 Websites appeared first on SecurityWeek.
Microsoft exec called AI scraping ‘the largest theft of labor in human history’
Microsoft exec called AI scraping 'the largest theft of labor in human history' Go to Source Article URL:...
OpenJev
OpenJev Go to Source Article URL: https://openjev.com/ Comments URL: https://news.ycombinator.com/item?id=49752041 Points: 5 # Comments: 1
British Army spends £16M on 1,000 pocket-sized eyes in the sky
The British Army is buying more than 1,000 small drones for battlefield surveillance and training under contracts worth £16 million ($21 million). The Ministry of Defence (MoD) says the new portfolio of "spy" drones will give soldiers better battlefield intelligence...
Claimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm Stealer
A financially motivated threat actor has been linked to the development and distribution of a JavaScript (JS)-based information stealer known as PhantomRaven via the npm package registry. "The developer likely wrote the malware using a large language model (LLM), an...
Critical Orkes Conductor Vulnerability Exploited in Attacks
CVE-2026-58138 is an unauthenticated remote code execution vulnerability that attackers can exploit via inline workflow definitions. The post Critical Orkes Conductor Vulnerability Exploited in Attacks appeared first on SecurityWeek.
AI systems don’t have a drive to survive. Here’s why
In controlled safety tests described earlier this year, researchers asked AI models to solve a series of simple math problems. Partway through the exercise, the instructors warned the bots that if they tried to solve the next problem, the computer environment they...
Royal Society slams UK.gov science shake-up
The president of the Royal Society has slammed the government’s decision to move science policy from the department also covering technology to the business department. In changes announced after Andy Burnham became UK Prime Minister in July, the government abolished...
Waymo is expanding to Singapore
Waymo has announced its next international location: Singapore.